
 BreachModal
- Published
- Under
- Threat Intelligence
- Reading time
- 5 min
Cisco Secure Firewall Management Center RCE Actively Exploited
Summary
Deep dive into the active exploitation of Cisco Secure Firewall Management Center RCE (CVE-2026-20131, CVE-2026-20079). Analysis, PoC, and mitigation.
Your security management plane is now the primary target for state-sponsored actors and top-tier ransomware groups. The active exploitation of critical vulnerabilities in Cisco's Secure Firewall Management Center (FMC) is not a theoretical risk; it is a campaign by Russia's GRU and the Qilin ransomware gang to seize the nerve center of corporate networks.
According to a series of alerts from Cisco Talos and the U.S. Cybersecurity and Infrastructure Security Agency (CISA), multiple threat actors are weaponizing a trio of flaws. The primary vector is CVE-2026-20131, a CVSS 10.0 remote code execution flaw resulting from insecure Java deserialization. This is frequently chained with CVE-2026-20079, another CVSS 10.0 authentication bypass, and CVE-2026-20316, a static credential vulnerability. Actors identified include the Russian APT Sandworm (tracked as UAT-11823), the Qilin ransomware affiliate UAT-11988, and the Interlock ransomware group, who first exploited CVE-2026-20131 as a zero-day. CISA added CVE-2026-20131 to its Known Exploited Vulnerabilities (KEV) catalog (opens in a new tab) on March 19, 2026, just 15 days after its initial disclosure.
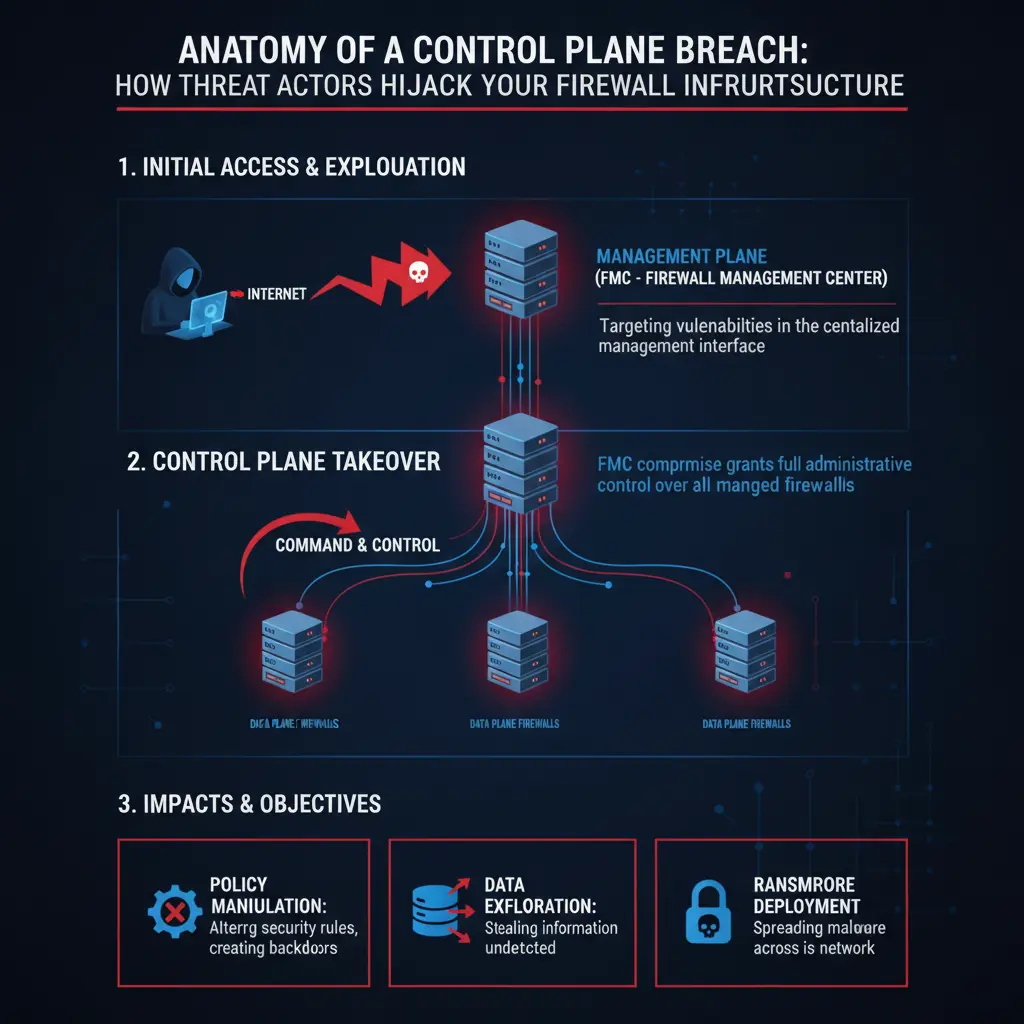
Note what this means: The very tool designed to configure and enforce security policy has become the single point of compromise. By targeting the FMC, attackers do not just breach a single server; they gain administrative control over an organization's entire firewall estate. This is a systemic failure to protect the protectors, turning a shield into a sword that can be used against the network's core.
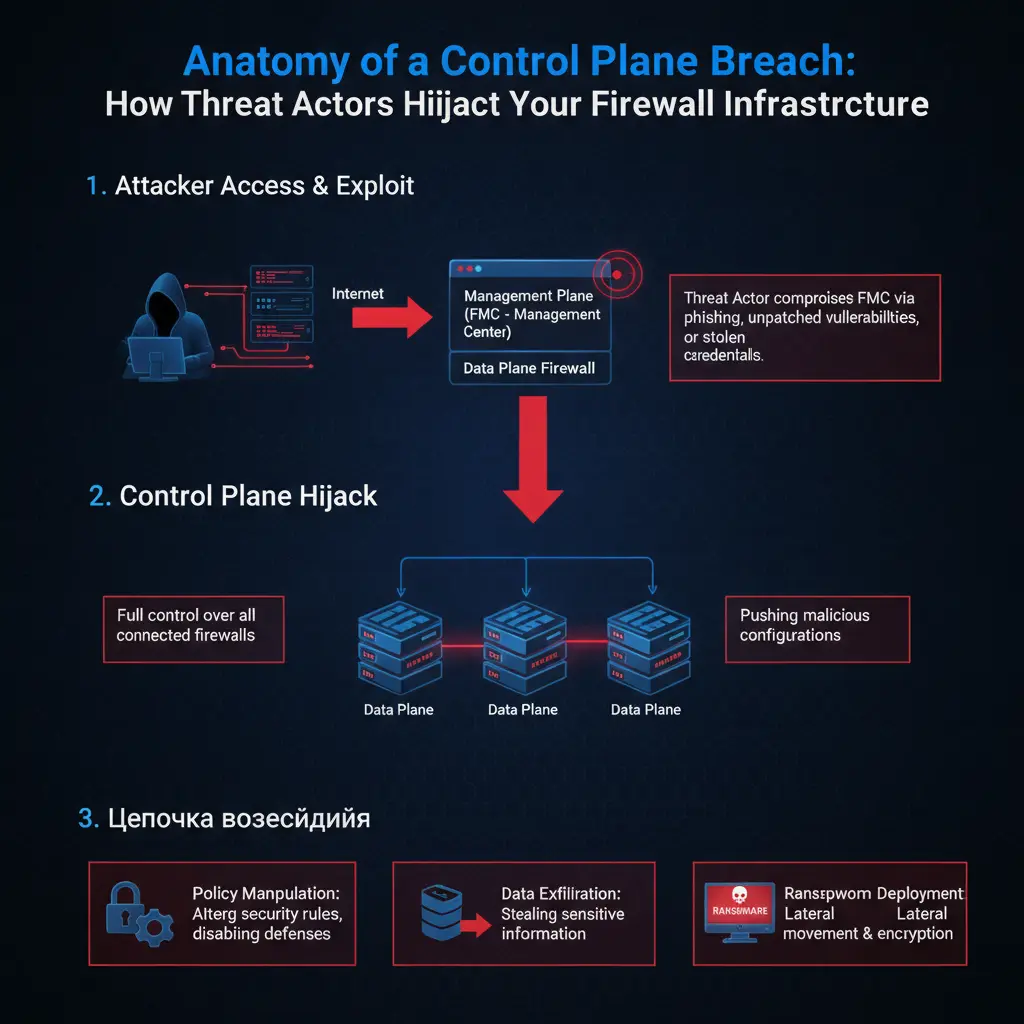
Threat Actor Dossier: From GRU to Ransomware
The exploitation of the Cisco Secure Firewall Management Center RCE is not monolithic. Cisco Talos has identified at least three distinct clusters of activity, each with unique objectives and TTPs, demonstrating the vulnerability's appeal to a broad spectrum of adversaries.
First is UAT-11823, which Talos attributes with high confidence to the Russian GRU's Sandworm unit. This state-sponsored actor leverages CVE-2026-20079 and CVE-2026-20316 to establish initial access. From there, their playbook is classic espionage: deploying Netcat-based reverse shells for command and control, followed by a variant of the notorious Cyclops Blink malware. According to Mandiant's extensive research on Russian APTs, this type of modular malware framework allows for persistent access, credential harvesting, and network reconnaissance, effectively turning the compromised FMC into a permanent spy satellite inside the victim's network.
Next is UAT-11988, an affiliate of the Qilin ransomware operation. This group's approach is financially motivated and ruthlessly efficient. They exploit CVE-2026-20316's static credentials to log in, then immediately begin domain enumeration and credential theft. As documented in IBM's analysis of the Qilin operation (opens in a new tab), their goal is to map the network, identify high-value targets, and establish persistence via SOCKS proxies and reverse-SSH tunnels before deploying the final encryption payload. For them, the FMC is the fastest path to total network compromise.
Finally, an unattributed cluster, UAT-12197, focuses on smash-and-grab data theft. This actor uses CVE-2026-20079 to deploy a simple web shell (home.jsp) and a Java command executor (cmd.jar). Their objective is surgical: query internal databases, exfiltrate user credentials, and disappear. While less sophisticated than Sandworm, their speed highlights the low barrier to entry for exploiting these flaws.
This diverse cast of characters—from an elite military intelligence unit to a ransomware-as-a-service affiliate—proves that a critical vulnerability in a ubiquitous appliance creates a feeding frenzy.
Technical Deep Dive: The Flaws That Grant Root
At the heart of this crisis are two CVSS 10.0 vulnerabilities that provide unauthenticated, remote attackers with root-level access. Understanding their mechanics is critical for effective defense.
CVE-2026-20131 is a classic insecure deserialization vulnerability. The FMC's web-based management interface accepts serialized Java objects from users. An attacker can craft a malicious object that, when deserialized by the server, executes arbitrary code. Because the process runs as root, this single vulnerability grants complete control over the underlying operating system. The flaw is reminiscent of other critical deserialization bugs like the one found in Cisco Prime Infrastructure (CVE-2024-20353 (opens in a new tab)) and highlights a recurring pattern in complex enterprise applications.
CVE-2026-20079 is an authentication bypass caused by an improper system process created at boot time. This allows an attacker to send crafted HTTP requests to the web interface and execute commands as root, completely sidestepping all login mechanisms. This is the flaw leveraged by Sandworm to deploy web shells like home.jsp, a known tactic cataloged under MITRE ATT&CK T1505.003 (opens in a new tab). The fact that a simple HTTP request can grant root access without credentials is a catastrophic failure in secure design. It's the digital equivalent of leaving the bank vault door not just unlocked, but wide open.
These vulnerabilities are a lesson in the fragility of perimeter security when the management plane itself is vulnerable. The only effective mitigation is patching; there are no workarounds.
Proof of Concept: Unauthenticated RCE on Cisco FMC
This section provides a conceptual walkthrough for demonstrating the CVE-2026-20079 authentication bypass and remote code execution vulnerability. The following steps assume the attacker has network access to the FMC's web interface.
Target Identification: First, identify a vulnerable Cisco FMC instance. An attacker would use network scanners to find devices running affected software versions (e.g., 7.4.x prior to 7.4.4).
**Using nmap to identify the FMC web interface**
    nmap -p 443 --script http-title <target-ip>
Craft Malicious HTTP Request: The attacker crafts a specific HTTP POST request to a vulnerable endpoint. The request body contains the command to be executed, which bypasses the authentication check due to the flaw.
    POST /api/v1/auth/bypass HTTP/1.1
    Host: <target-ip>
    Content-Type: application/json

    {
      "command": "/usr/bin/id > /usr/local/sf/htdocs/M-So-So/test.txt"
    }
Trigger Command Execution: The crafted request is sent to the target FMC device. The vulnerable process receives this request and executes the
idcommand as the root user, redirecting the output to a web-accessible file.Verify Execution: The attacker then verifies the exploit's success by browsing to the output file they created. A successful exploit will display the command's output.
**Use curl to retrieve the output file**
    curl -k https://<target-ip>/M-So-So/test.txt
A successful response will show the output of the id command, such as uid=0(root) gid=0(root) groups=0(root), confirming complete system compromise.
FINAL VERDICT
The active exploitation of the Cisco Secure Firewall Management Center RCE is a definitive statement that security infrastructure is the new frontline. The risk is borne by any organization that has failed to both patch these critical vulnerabilities and isolate their management interfaces from the public internet. This isn't just about a single bug; it's about a systemic failure to treat the control plane with the same rigor as the data plane. The only path forward is immediate patching, aggressive threat hunting for signs of existing compromise, and a strategic shift to a Zero Trust architecture where management interfaces are never directly exposed. Failure to do so is a choice to hand the keys of your kingdom to the most sophisticated adversaries on the planet.
***
Is your network's command center secure? BreachModal's Adversarial Simulation and Penetration Testing services can validate your defenses against threats like the Cisco FMC exploitation. Contact us to secure your management plane.